Third-Party Risk Management (TPRM)
Take control of vendor risk with third-party risk management.
Centralize, communicate, and mitigate. Standardize vendor assessments, give teams and vendors one place to stay aligned, and connect vendor risk to the controls, risks, findings, decisions, and remediation it affects across the organization.
Are fragmented tools making vendor risk chaotic?
Managing third-party risks can be overwhelming when you rely on multiple tools and manual processes. Without centralized communication, your teams and vendors operate in silos - increasing the risk of compliance gaps, inefficiencies, and missed assessments. Keeping track of vendor compliance should not slow down your operations.
Cyturus helps you standardize and streamline vendor risk management while preserving the complete record of each vendor issue: what was identified, who owned it, what decision was made, what action followed, and how it affected your control environment.
Why It Matters
Reduce vendor risk assessment time by 90% and improve collaboration.
One control architecture. Vendor risk connected to everything else.
At Cyturus, third-party risk does not live in a separate program. Vendor assessments, findings, risks, decisions, remediation, and evidence connect to the same governed control record as compliance and internal risk, so a vendor issue becomes part of the organization’s complete governance history instead of another isolated workstream.
Connect vendor findings to the controls and risks they affect
Track ownership, decisions, remediation, and evidence in one record
Reuse vendor and control information across compliance, risk, and assessments
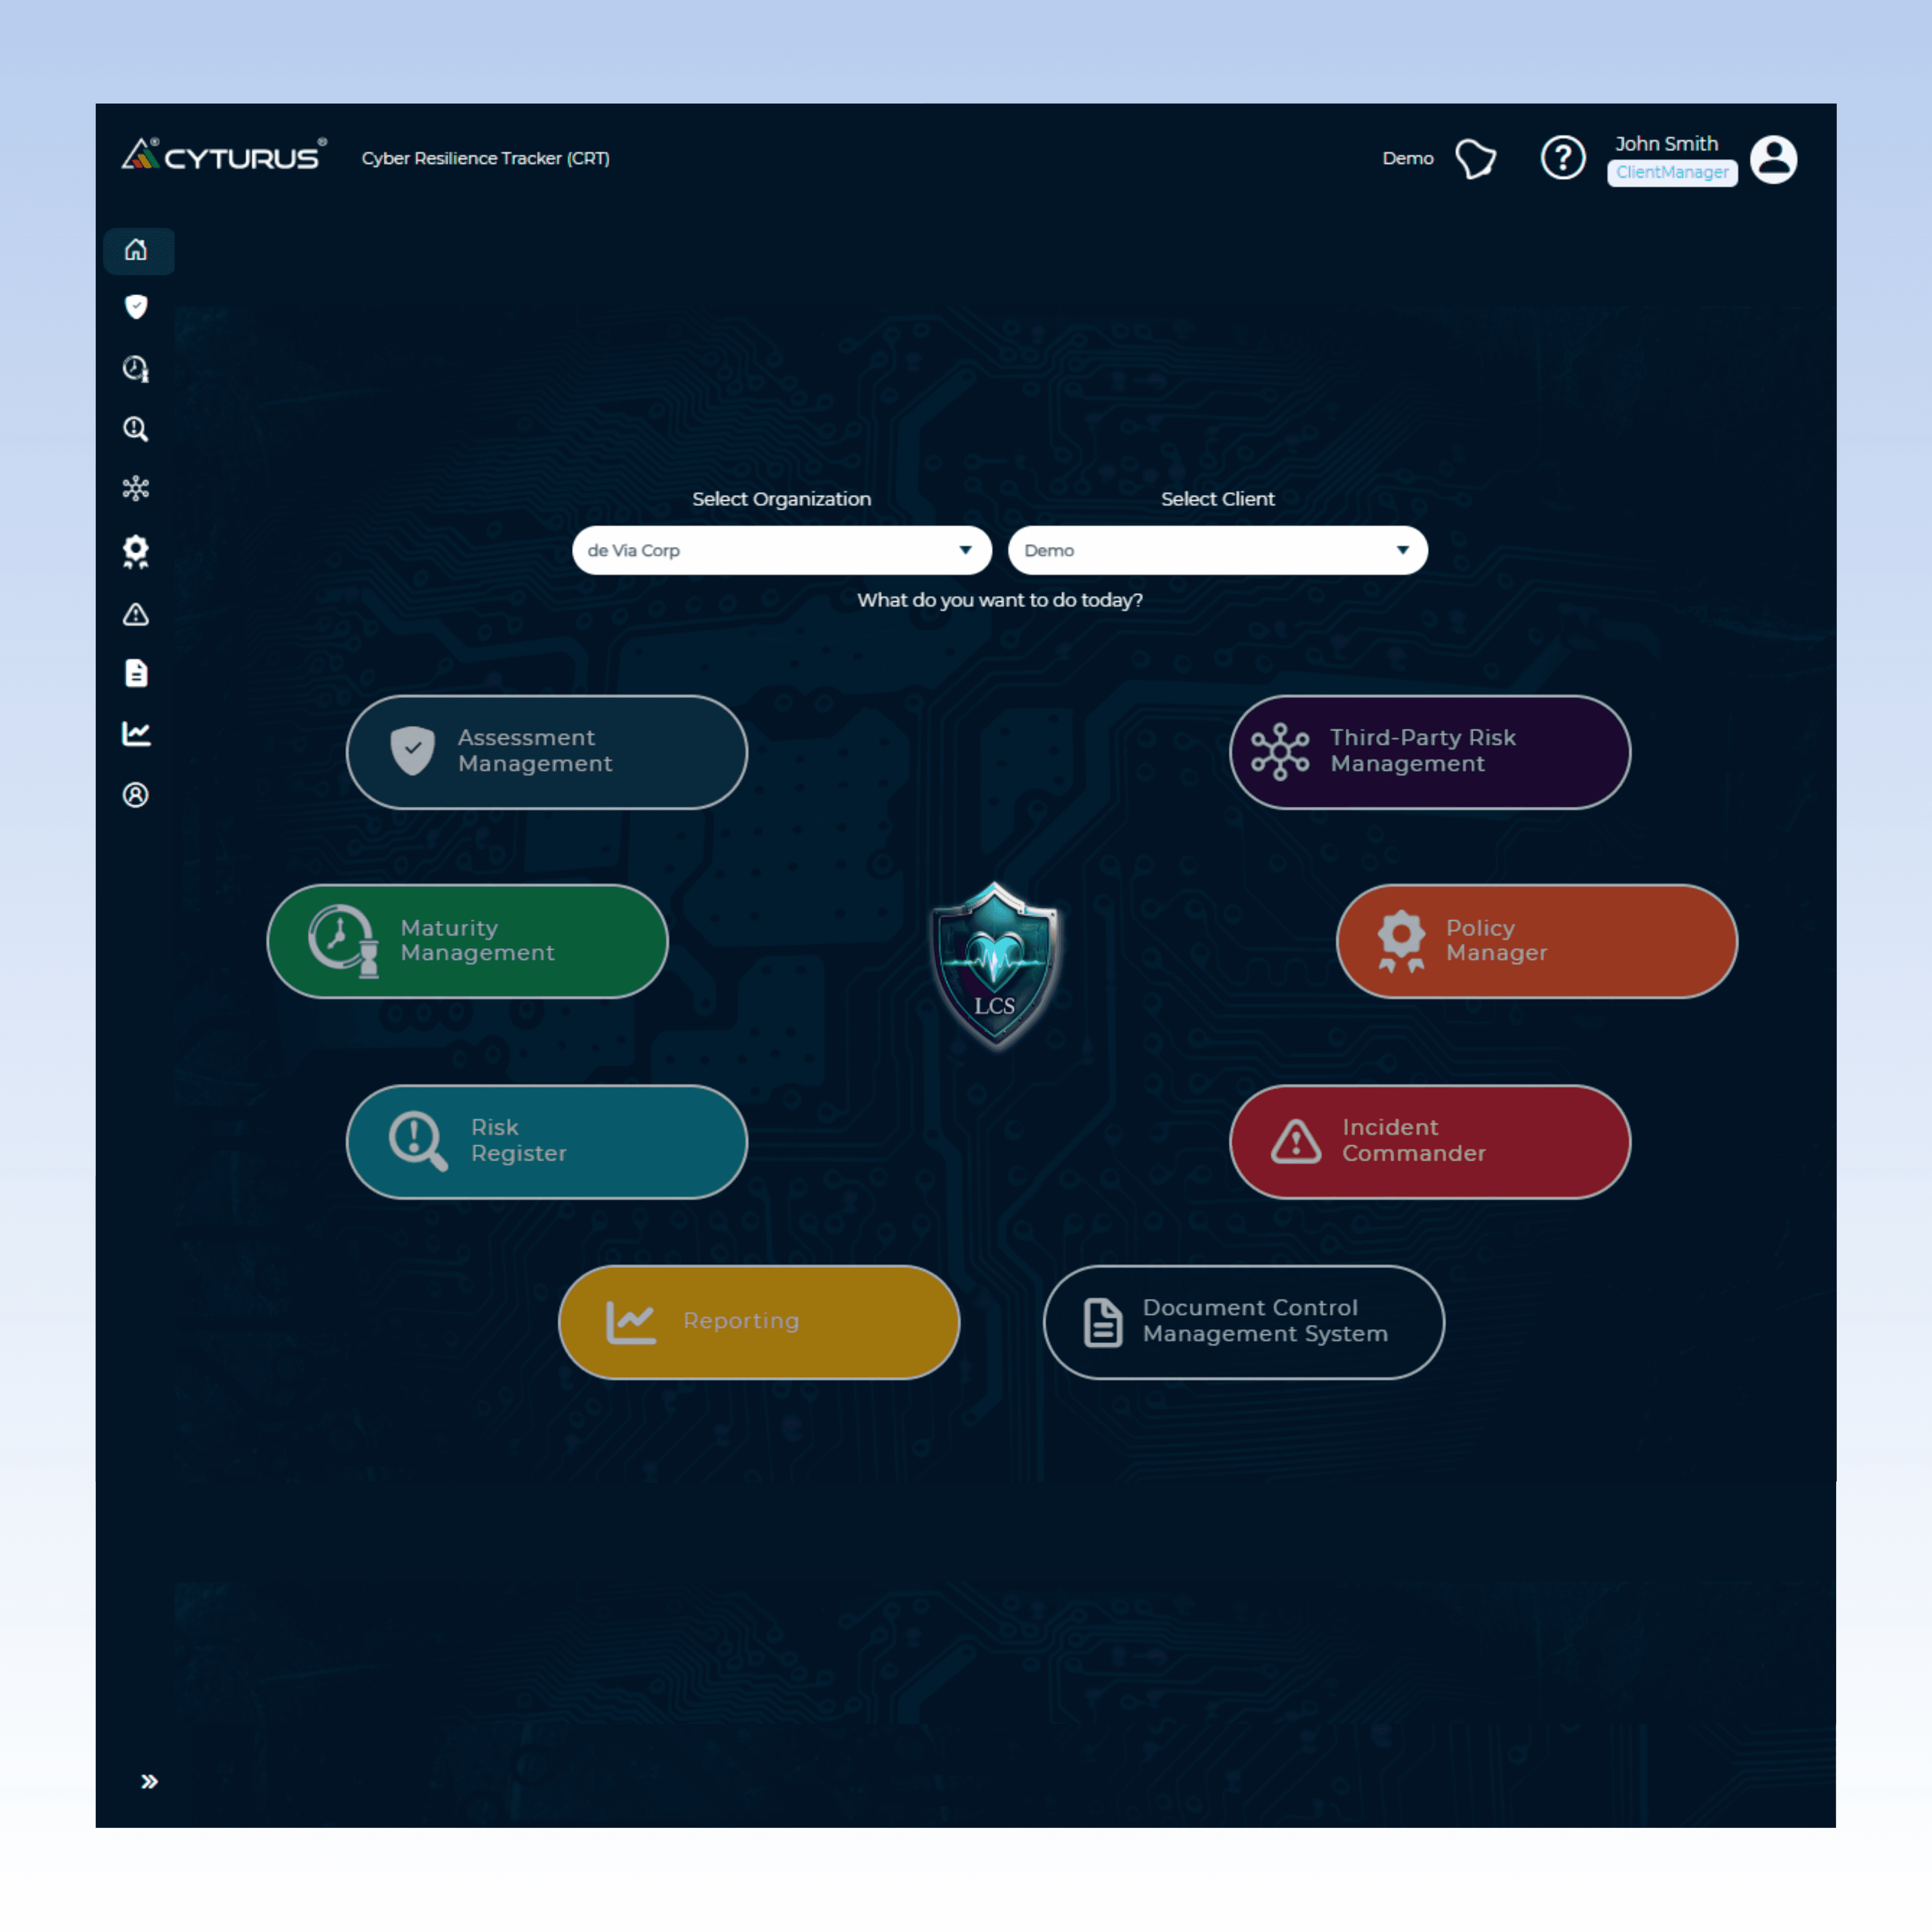

See Cyturus Cyber Resilience Tracker in Action
Bring your frameworks. We'll show you how a single control answer maps everywhere and where your real maturity stands today.
No rip-and-replace · Works alongside your existing program · Built by practitioners