Risk Register
Take control of your cybersecurity risk.
Quantify, track, and manage risks as they are identified. The Risk Register preserves the ownership, decisions, actions, and history behind each risk and connects it to the compliance, third-party, findings, and remediation activities that surface it.
Relying on outdated risk logs that can’t keep up?
Cybersecurity risks evolve quickly, but many organizations still rely on static risk logs that become outdated as new findings, assessments, incidents, and third-party issues emerge. Without a structured way to quantify, update, and track identified risks over time, it becomes difficult to maintain a reliable view of the organization’s risk posture.
Cyturus helps you register, evaluate, prioritize, and manage risks as they are identified, while preserving the ownership, decisions, actions, and history behind them.
Why It Matters
Reduce manual tracking and maintain a current, defensible view of identified risk.
One control architecture. Risk connected to everything else.
At Cyturus, risk does not live in a separate register. Registered risks connect to the same governed control record as compliance, third parties, findings, incidents, evidence, and remediation, so every risk decision becomes part of the organization’s complete governance history.
Connect registered risks to the controls, findings, incidents, and third parties they relate to
Track ownership, treatment decisions, remediation, and evidence in one record
Preserve the history behind risk acceptance, mitigation, and escalation
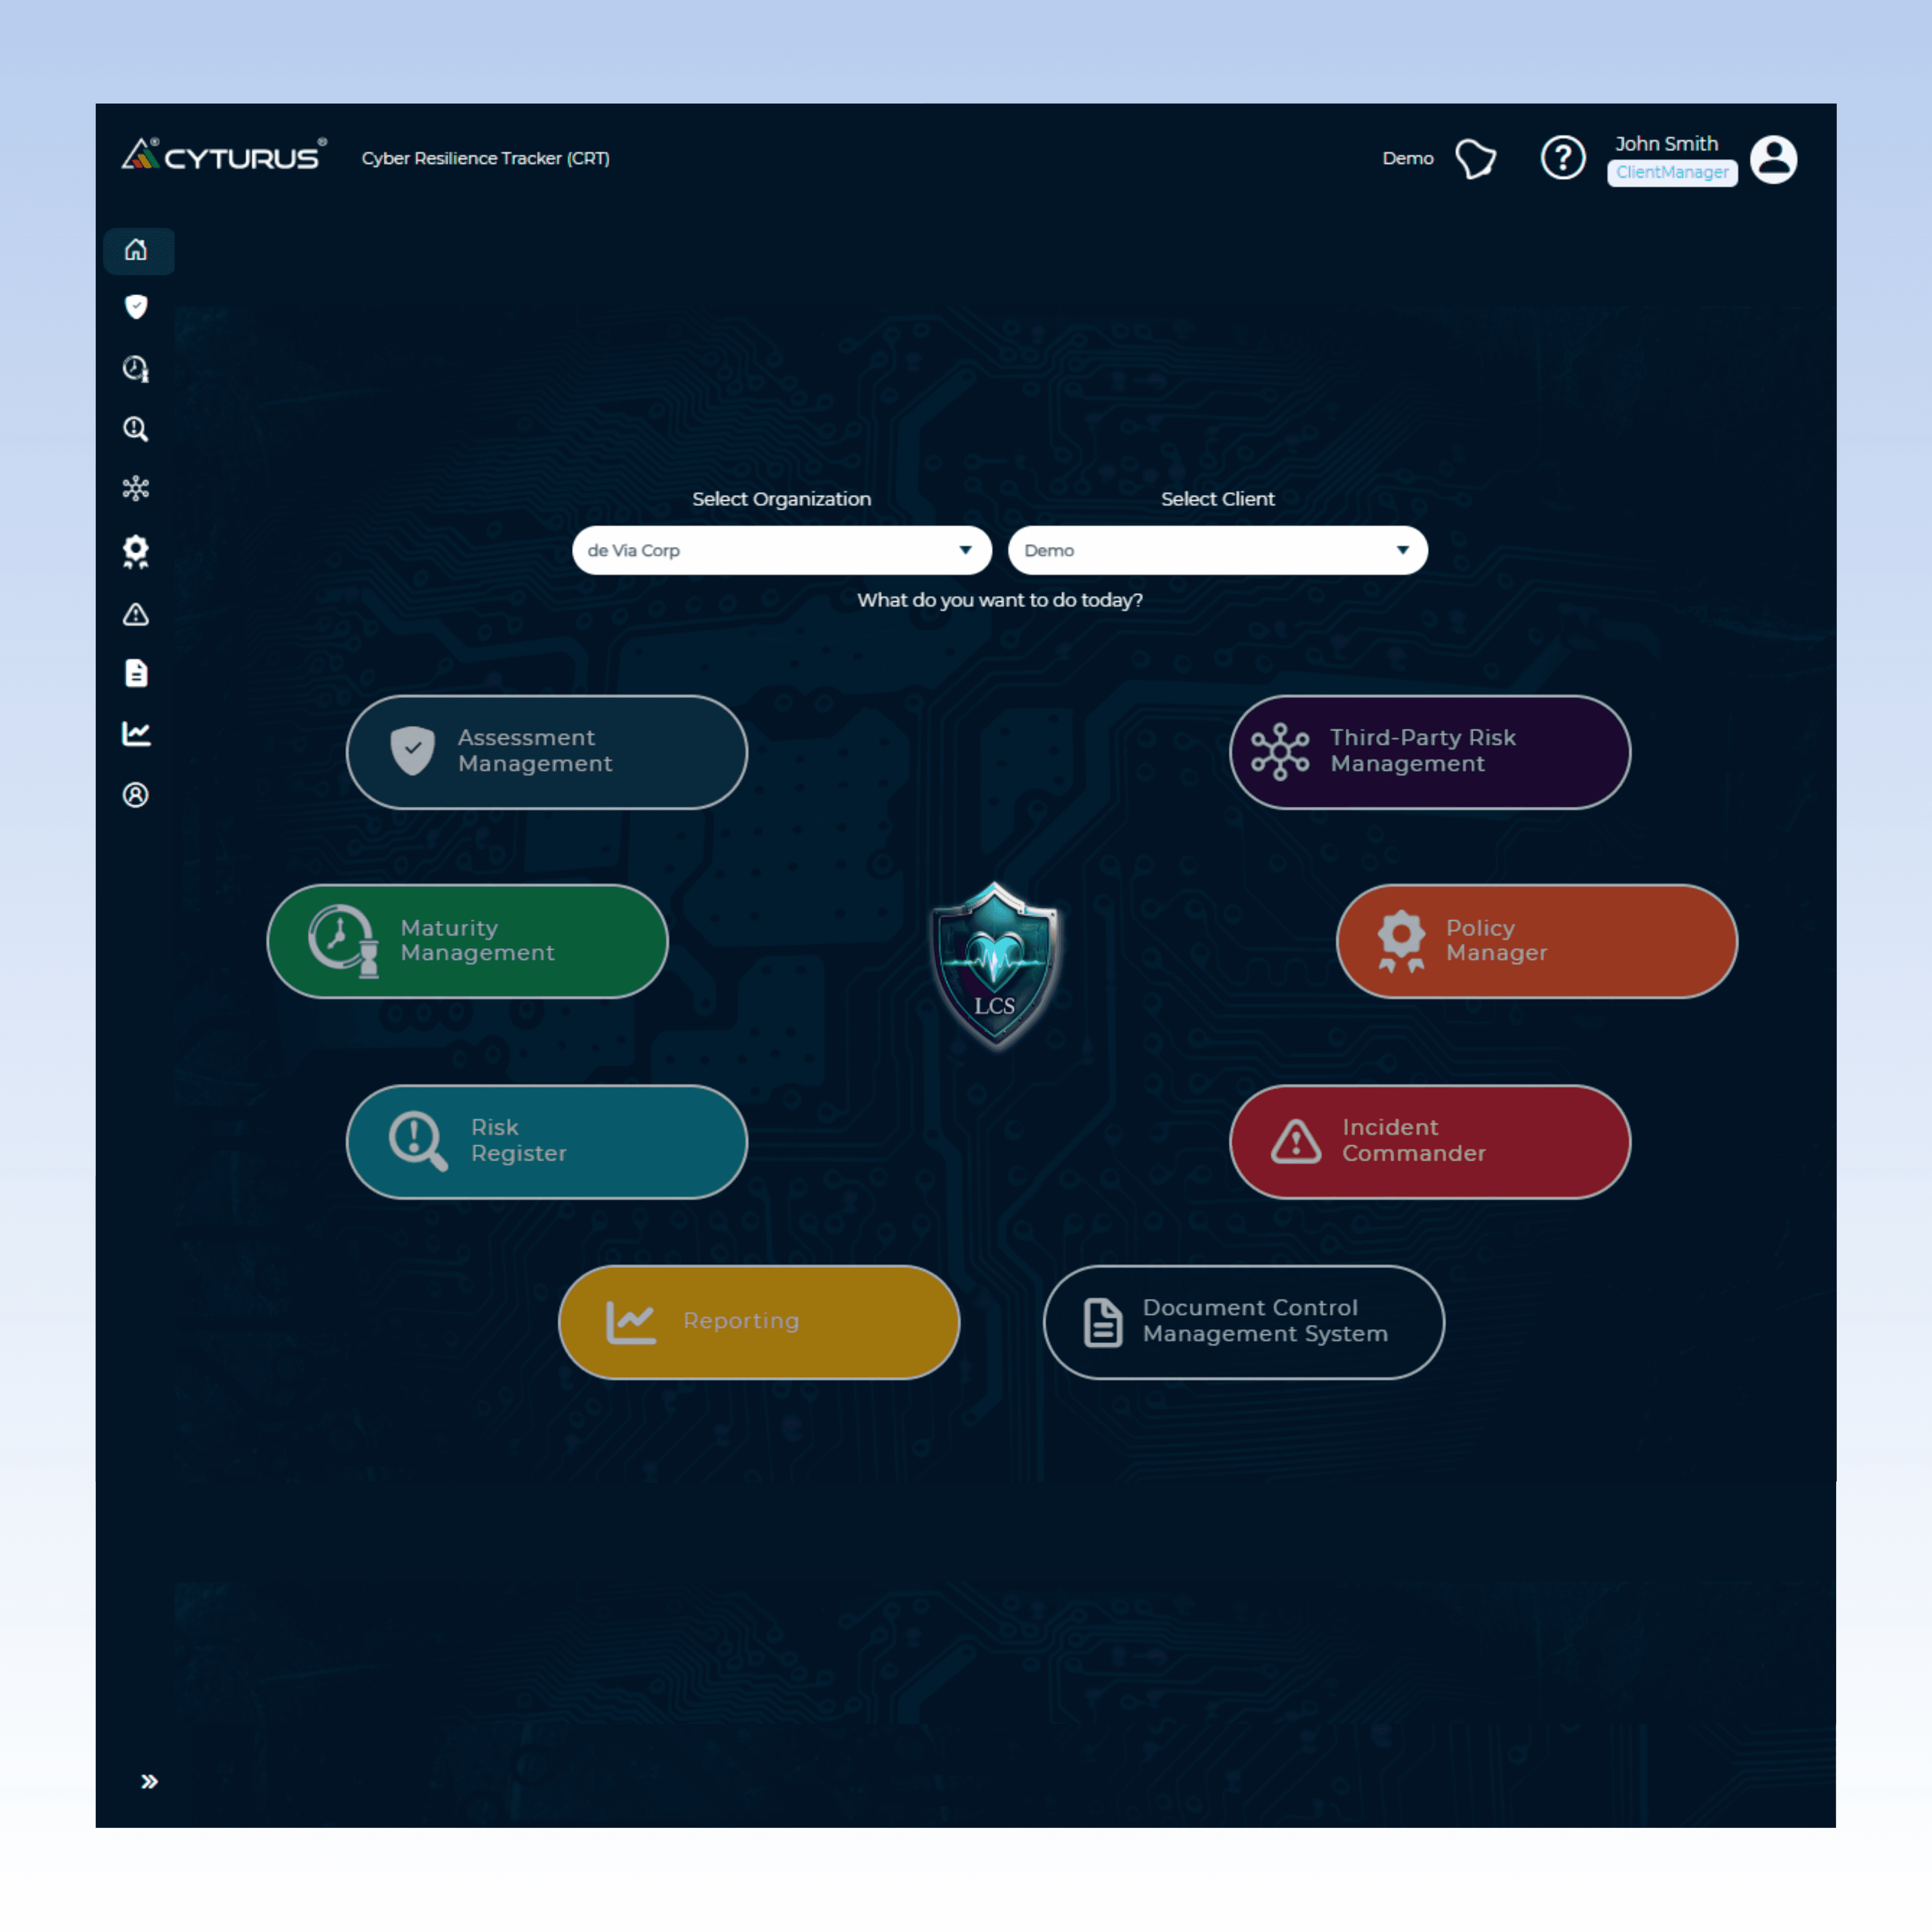

See Cyturus Cyber Resilience Tracker in Action
Bring your frameworks. We'll show you how a single control answer maps everywhere and where your real maturity stands today.
No rip-and-replace · Works alongside your existing program · Built by practitioners