Visual element used in the Header & Footer/Header component

Cyber Maturity Index (CMI)

One number that proves your cybersecurity maturity is growing.

The Cyber Maturity Index (CMI) is an advanced approach to measuring cybersecurity maturity. Unlike traditional risk assessments that give a static, point-in-time evaluation, the CMI lets you track and improve your posture continuously - a quantifiable score built on the same governed control record your compliance and risk programs use.

What is the Cyber Maturity Index?

The CMI measures the capacity (what) and effectiveness (how well) of your cybersecurity processes, systems, and controls. It evaluates how well security practices are implemented and monitors improvements over time - ideal for strategic planning and long-term maturity tracking.

The CMI focuses on root causes and trends, tracking the evolution of cybersecurity risk over time and giving you a defensible record of how your security posture is changing and why.

Patented Algorithm

Patented Quantitative Scoring

Cyturus uses a proprietary algorithm to generate a CMI Score, quantifying security effectiveness and progression over time.

Patented Algorithm

Patented Quantitative Scoring

Cyturus uses a proprietary algorithm to generate a CMI Score, quantifying security effectiveness and progression over time.

Repeatable

Continuous Optimization

Cyturus ensures security controls are documented, repeatable, measured, and continuously improved.

Repeatable

Continuous Optimization

Cyturus ensures security controls are documented, repeatable, measured, and continuously improved.

Root Causes & Trends

Strategic, Not a Snapshot

Cyturus tracks the evolution of cybersecurity risk over time, ideal for strategic planning and long-term maturity.

Root Causes & Trends

Strategic, Not a Snapshot

Cyturus tracks the evolution of cybersecurity risk over time, ideal for strategic planning and long-term maturity.

The Other Half of the Picture

What is a risk assessment?

Qualitative scoring

Uses an industry-standard 5×5 matrix for Likelihood × Impact.

Quantitative scoring

Calculates potential business impact using Likelihood × Frequency combined with the financial component.

Point-in-time

A traditional assessment captures risk at a single moment - useful, but not continuous.

How CMI and risk assessments work together.

Rather than replacing risk assessments, the CMI extends their value by showing how control capability and effectiveness change over time.

CMI scores the capability, effectiveness, and consistency of controls over time

Risk assessments identify and prioritize remediation for immediate threats

Together they give a holistic view of your cybersecurity resilience

One control architecture. Maturity scoring connected to everything else.

Visual content on the Use Cases Cyber Maturity Index

Why CMI?

Why choose CMI for continuous compliance?

Continuous compliance model

Provides an ongoing assessment rather than a one-time snapshot, so your posture is always current.

Data-driven decisions

Make informed, strategic security decisions based on real-time insights instead of guesswork.

Clear executive reporting

CMI scores help security teams communicate progress effectively to leadership and the board.

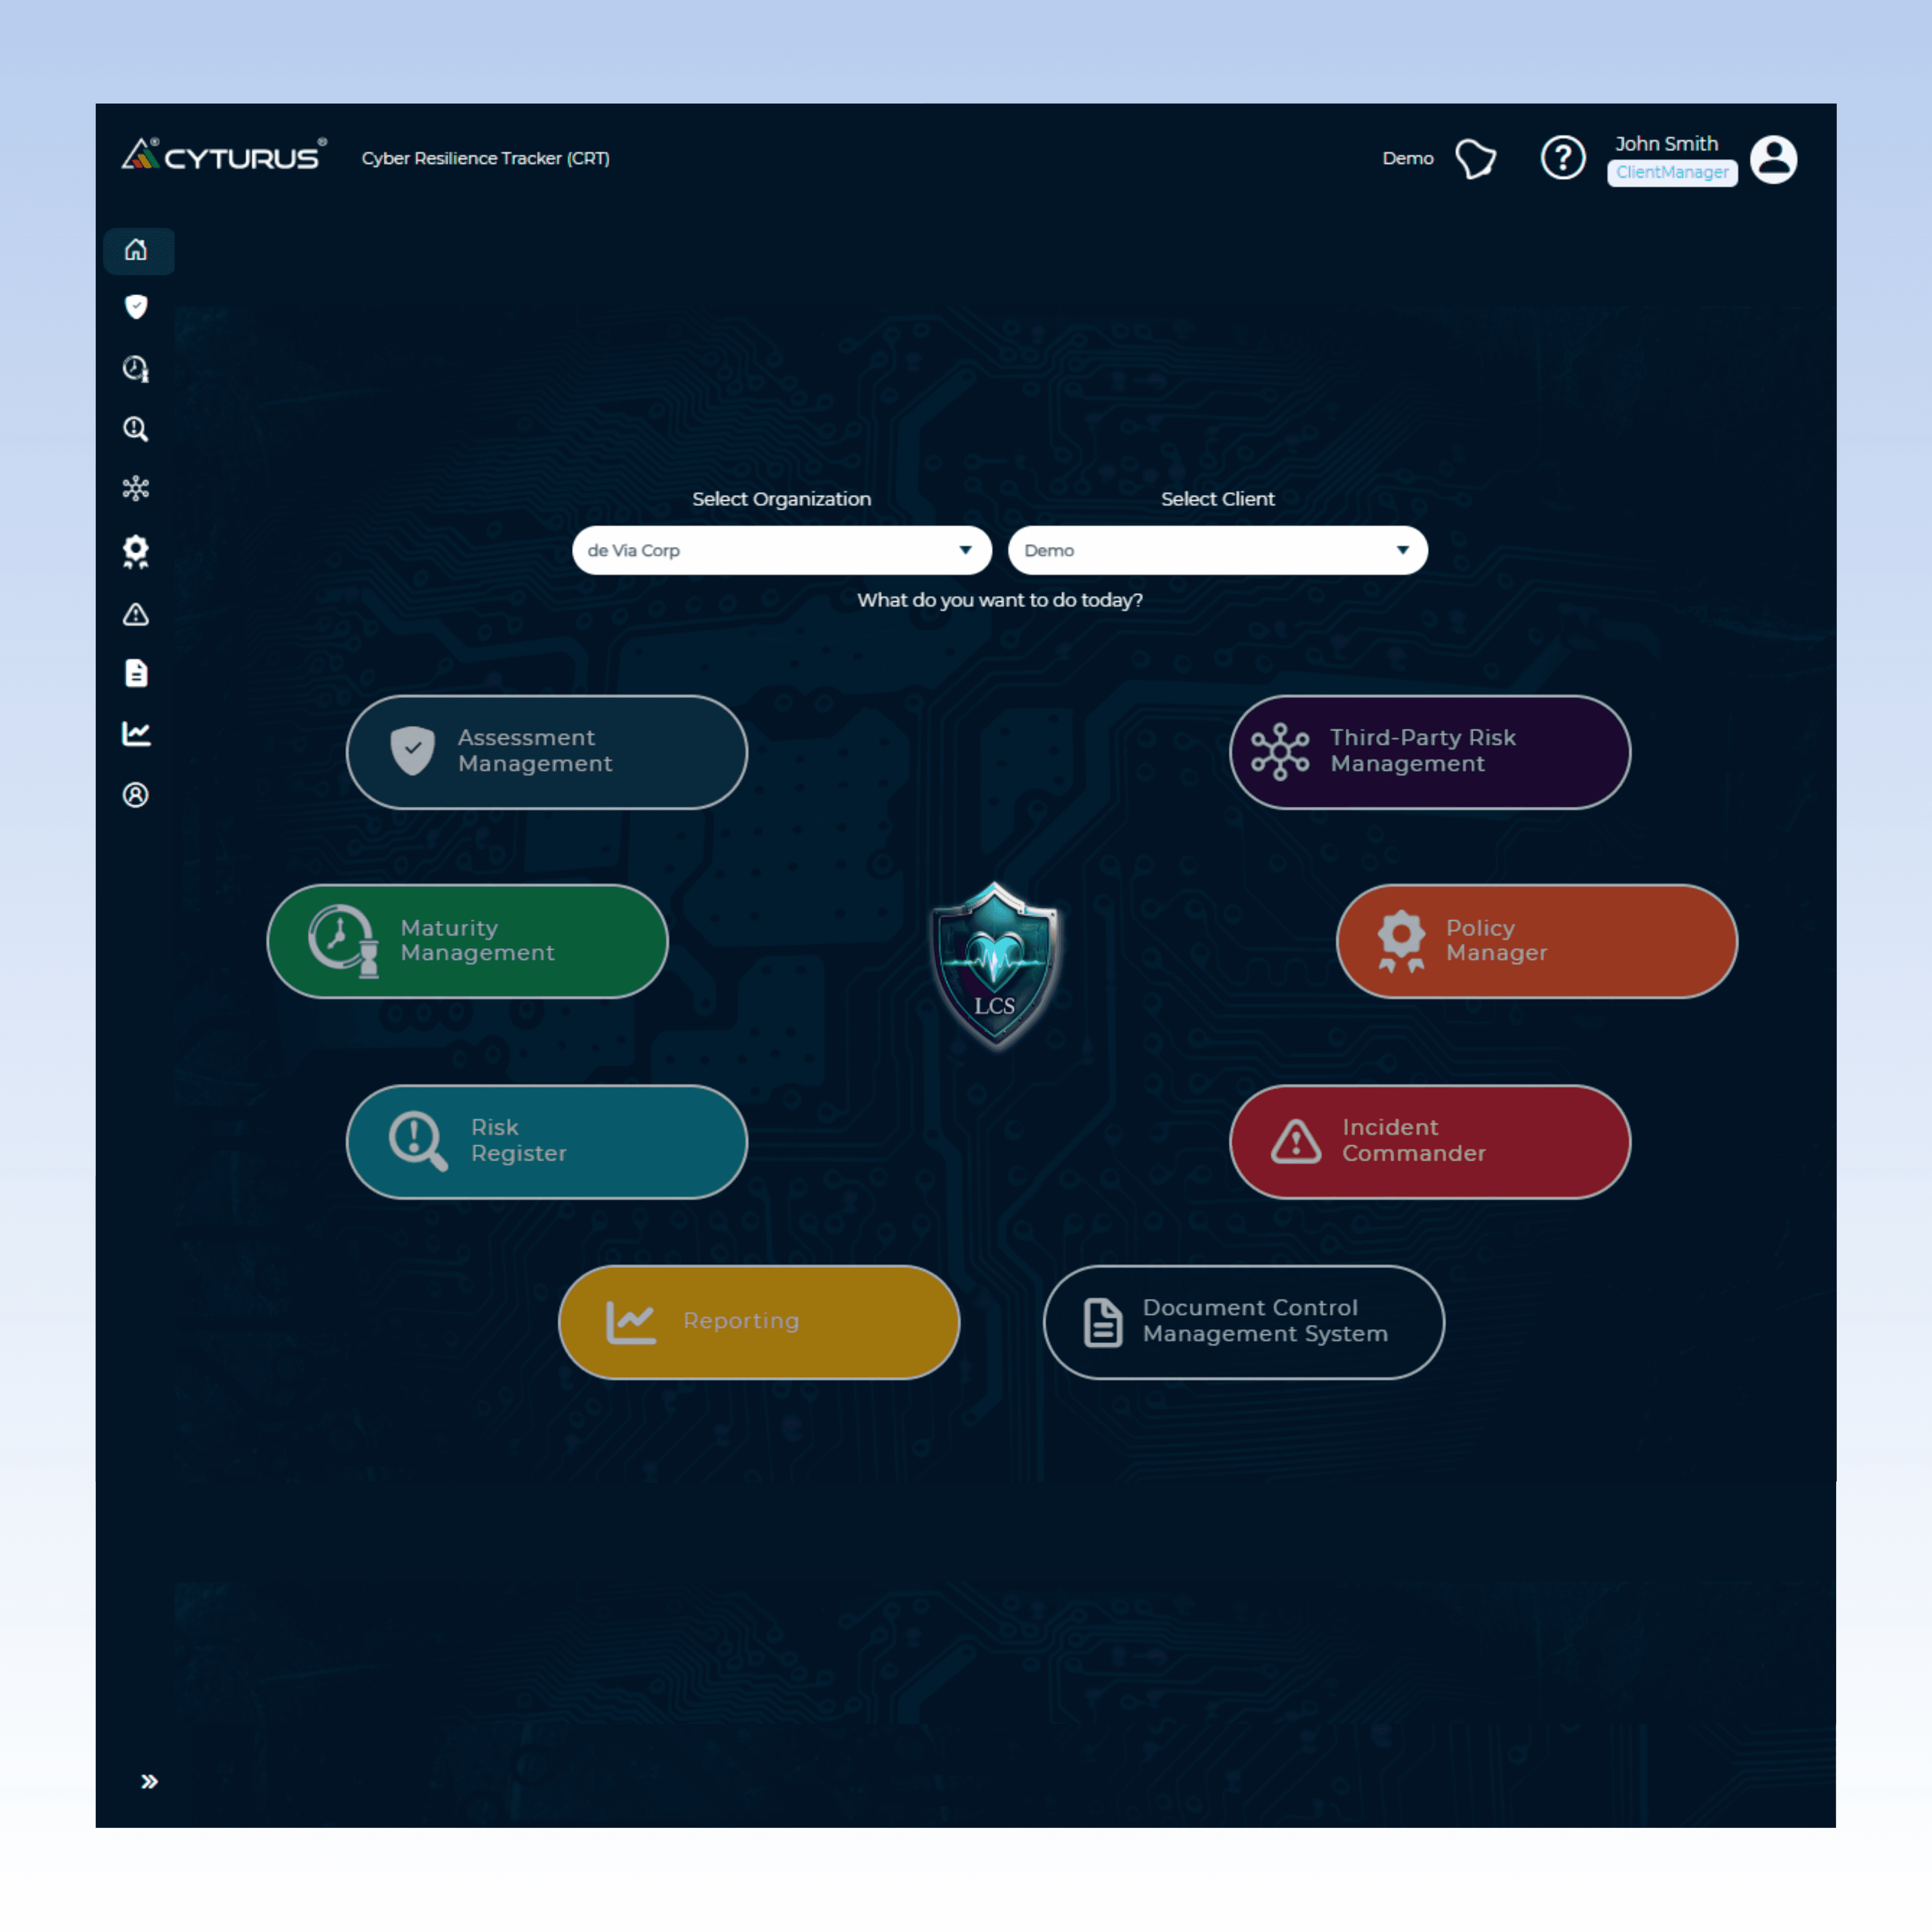
One control architecture. Maturity scoring connected to everything else.

At Cyturus, maturity, compliance, and risk do not live in separate programs. Maturity scoring reads from the same governed control record as risk, compliance, findings, evidence, and remediation, so every score is grounded in the organization’s actual control environment and the history behind it.
Visual element used in the Features/Feature Illustration #3 component

Loved by Enterprises

See How Leaders Like You Run Continuous Compliance and Risk Management

Visual element used in the Misc/Testimonials Section component

"Cross-control risk visibility is what most other tools don't allow you to do. Instead of doing 100% of the work again for a new framework, you're doing 20%. The risk piece is what separates this." 

Robert Groome

CIO, USC School of Engineering

Loved by Enterprises

See How Leaders Like You Run Continuous Compliance and Risk Management

Visual element used in the Misc/Testimonials Section component

Robert Groome

CIO, USC School of Engineering

"Cross-control risk visibility is what most other tools don't allow you to do. Instead of doing 100% of the work again for a new framework, you're doing 20%. The risk piece is what separates this." 

Robert Groome

CIO, USC School of Engineering

See Cyturus Cyber Resilience Tracker in Action

Bring your frameworks. We'll show you how a single control answer maps everywhere and where your real maturity stands today.

No rip-and-replace · Works alongside your existing program · Built by practitioners